Security from Zero
Your first steps toward a blue-team job.
A practical starting point for a SOC analyst or junior security analyst role. Learn the computer basics, build investigations you can explain, and turn that work into applications and interview answers.
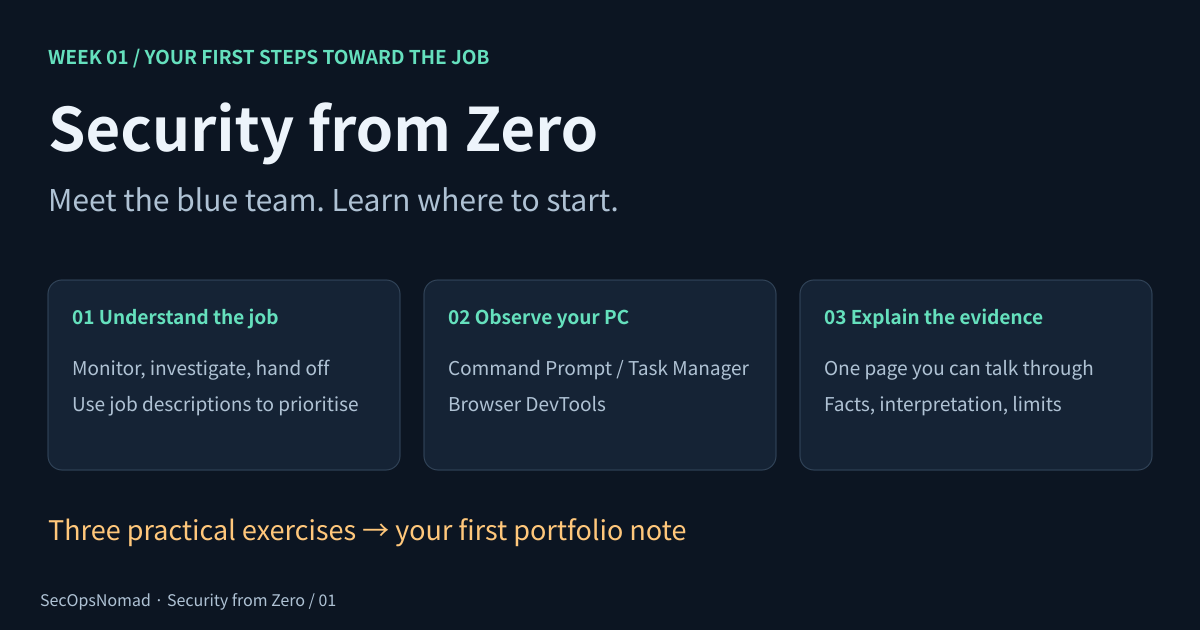
Your first investigation starts on your own PC.
Meet the blue team. Use Command Prompt, Task Manager and browser DevTools to see what normal activity looks like.
7-day plan / about 5 hours / one evidence note
Read Week 1Start with what you have
Week 1 needs a Windows PC and a browser. No certification or paid security tool required.
Leave with evidence
A case note, a log timeline, a reasoned decision: something you can discuss in an application.
Explain your reasoning
Separate what you observed, what you think it means, and what you still need to check.
Study toward a role
Use real job descriptions in your region to choose what to learn next.
15 topics, each with something to show
Published topics are linked below. Remaining topics are planned; release dates are not set. Take the time you need for each skill. Completing the series does not guarantee employment.
- Topic 01Read
What blue team does, and where to start
Understand the analyst’s job, inspect your own computer and write your first evidence note.
- Topic 02Read
Networking an analyst actually uses
Read an IP address, port, DNS answer and web request, and explain how they connect.
- Topic 03Read
Operating systems, users and permissions
Navigate files, inspect permissions and distinguish users, processes and services.
- Topic 04Read
Read your first security logs
Build a small timeline and separate an observed event from your interpretation.
- Topic 05Planned
Accounts, authentication and access
Explain MFA, least privilege and common reasons a sign-in needs investigation.
- Topic 06Planned
Triage a suspicious email
Assess a message, document the evidence and recommend the next check.
- Topic 07Planned
Find evidence in a SIEM
Filter a bounded log sample and explain what a search can and cannot show.
- Topic 08Planned
Investigate an endpoint alert
Follow a process tree and identify the context needed before escalating.
- Topic 09Planned
Make and explain a triage decision
Assess severity, identify missing evidence and write a clear handoff.
- Topic 10Planned
Use threat intelligence with context
Check an indicator’s source and age, and map behavior without overstating it.
- Topic 11Planned
Your role in incident response
Separate investigation from containment and know when to involve a senior analyst.
- Topic 12Planned
Automate one useful analyst task
Parse a small log file and check your result against a manual count.
- Topic 13Planned
Build a portfolio case someone can review
Publish a reproducible investigation with evidence, limits and next steps.
- Topic 14Planned
Turn your work into applications
Match genuine project evidence to a role and write accurate CV bullets.
- Topic 15Planned
Work a case and explain it in an interview
Present your reasoning, handle follow-up questions and plan your next skill gap.